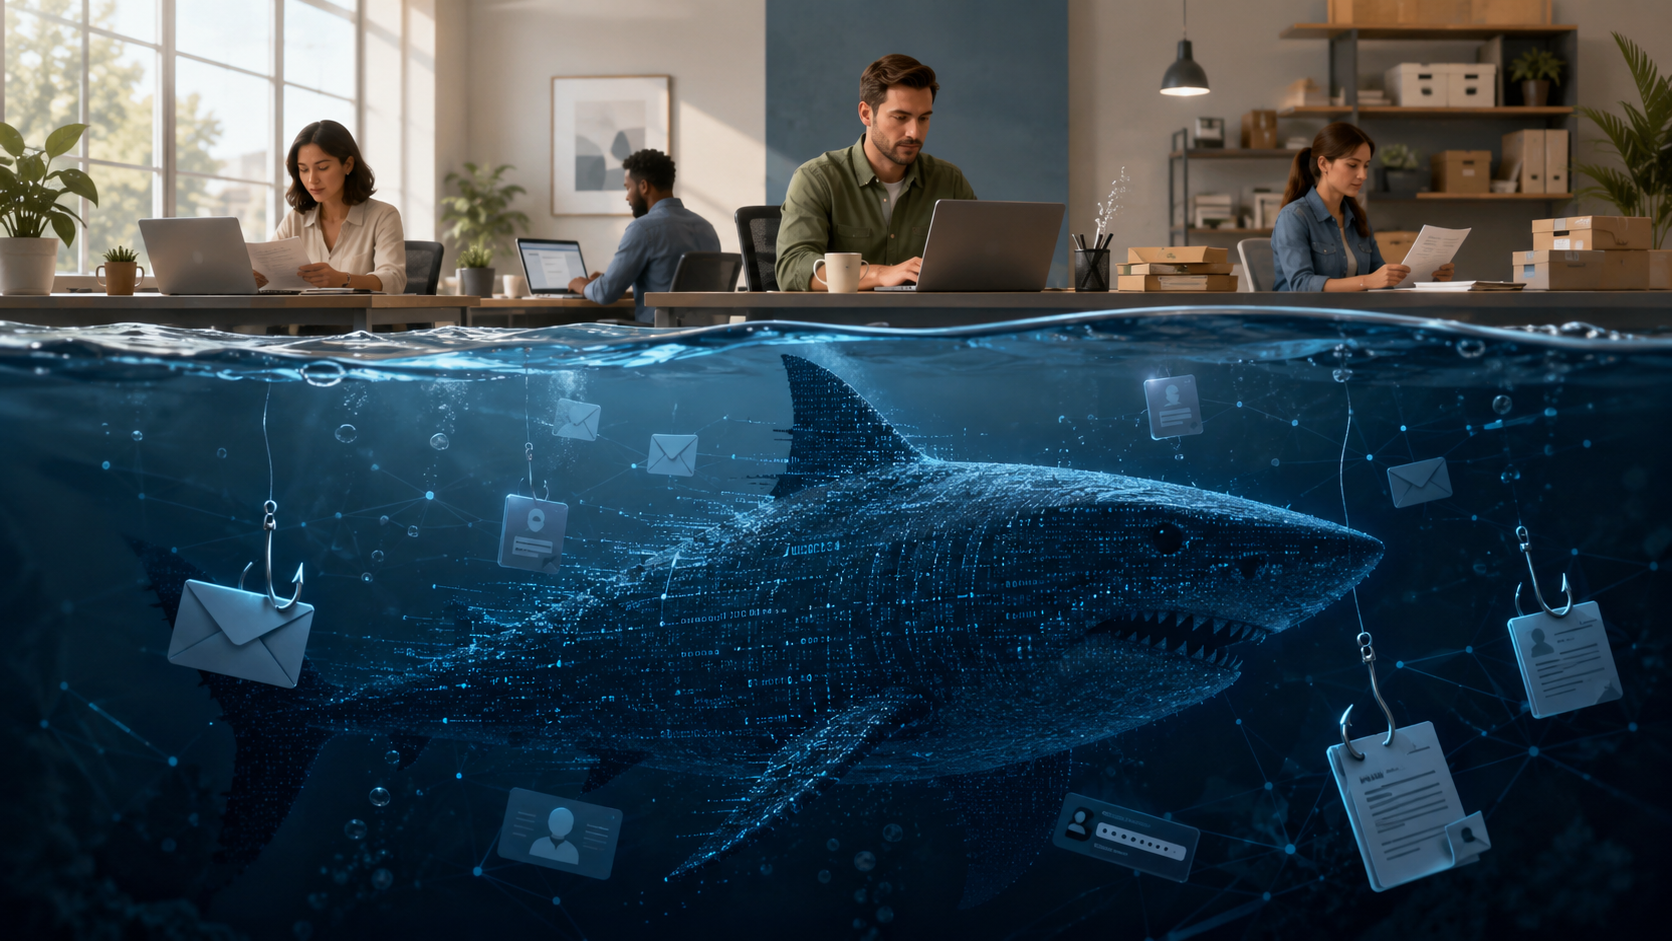
Small-business owners have enough visible problems to manage every day.
You can see when a project is falling behind, when an employee calls in sick, or when a customer payment is late. Cybersecurity threats are different. They are often designed to blend into normal business activity until money is stolen, information is exposed, or your systems stop working.
On the surface, everything may appear calm. Underneath, however, an attacker could be studying your employees, vendors, and daily routines while waiting for the right moment to strike.
This risk can become even greater during the summer, when employees are traveling, schedules are changing, and managers may be away from the office.
Here are three hidden cybersecurity risks every small business should be watching.
1. Fake Invoices and Vendor Impersonation
A cybercriminal does not always need to break through your firewall or install malware.
Sometimes, all they need is one convincing email.
In a business email compromise attack, a criminal pretends to be someone your employees already trust. That could be:
- A regular supplier
- A company executive
- A customer
- A payroll provider
- A contractor
- A financial institution
The email may look completely normal. It might ask an employee to pay an invoice, change a vendor’s banking information, purchase gift cards, or urgently approve a wire transfer.
These attacks are especially effective when the employee who normally approves payments is unavailable. A temporary replacement may not recognize that the request is unusual, and the attacker may create a sense of urgency to discourage verification.
How small businesses can reduce the risk
Create a simple verification policy for financial requests.
Employees should independently confirm any request involving:
- New payment instructions
- Changes to bank account information
- Unexpected wire transfers
- Large or unusual purchases
- Urgent payments requested by email
The confirmation should be made by calling a trusted phone number already on file—not a phone number included in the suspicious email.
A two-minute phone call can prevent a very expensive mistake.
2. Phishing Attacks That Target Busy Employees
Phishing attacks work because employees are busy.
A team member may receive what appears to be a Microsoft 365 password-reset notice while rushing into a meeting. Another employee may get a text message that looks like it came from the owner. Someone in accounting may receive an urgent request to approve a payment before the end of the day.
The goal is to make the employee act before thinking.
Common warning signs include:
- Unexpected password-reset messages
- Login requests you did not initiate
- Urgent payment instructions
- Unfamiliar links or attachments
- Messages asking you to bypass normal procedures
- Requests for passwords or verification codes
The most important defense is not simply another piece of software. It is creating a workplace where employees feel comfortable slowing down and asking questions.
Attackers use urgency as a weapon. When employees pause and verify unusual requests, that weapon becomes much less effective.
Build a security-aware culture
Remind employees that they will not get in trouble for questioning a suspicious request—even when the message appears to come from an owner, manager, or important customer.
Provide regular security-awareness training and make it easy for employees to report suspicious messages. Your team should know exactly who to contact when something does not feel right.
3. Vendors and Third Parties With Too Much Access
Your cybersecurity risk does not stop at your front door.
Small businesses often rely on outside vendors for accounting, payroll, software, cloud services, marketing, maintenance, and IT support. Many of those providers may have access to company data, email accounts, cloud applications, or internal systems.
When one of those vendors is compromised, the attacker may be able to use that trusted connection to enter your business.
Former contractors and service providers can create risk too. An account that was never disabled after a project ended may remain active for months or years.
Small businesses should be able to answer three basic questions:
- Which vendors can access our systems or information?
- What applications, accounts, or data can they access?
- Who inside our company is responsible for reviewing that access?
The original source emphasizes that outsourced services do not eliminate your responsibility to understand and manage this exposure.
Review vendor access regularly
At least once or twice a year, review:
- Active vendor accounts
- Administrator permissions
- Remote-access tools
- Shared passwords
- Connected cloud applications
- Former employee and contractor accounts
- Service providers that are no longer being used
Remove any access that is no longer necessary and require multifactor authentication wherever possible.
Do Not Wait for an Obvious Warning Sign
Many small businesses assume they are secure because nothing appears to be wrong.
Unfortunately, cybercriminals rarely announce themselves. They may quietly monitor an email account, study payment routines, or maintain access to a system until they find the best opportunity to act.
That is why cybersecurity should not be treated only as an emergency response.
A small business needs ongoing monitoring, clear financial procedures, employee training, reliable backups, strong account security, and regular reviews of vendor access.
The goal is to find the danger before it reaches the surface.
A professional cybersecurity assessment can help identify weaknesses across your employees, vendors, devices, and everyday business operations before those weaknesses turn into downtime or financial loss.